Critical GitLab Vulnerability Under Active Exploitation by Hackers
Security agencies warn that a high-severity flaw is being actively used in cyberattacks.
A Critical Threat to GitLab Users
A critical security flaw in the popular DevSecOps platform GitLab has become a major threat. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that the vulnerability, tracked as CVE-2026-97229, is already being exploited by malicious actors. Discovered earlier this month, the flaw allows unauthorized access and arbitrary code execution.
The issue stems from how CI/CD configuration files process regular expressions. Due to insufficient validation, attackers can use specially crafted regular expressions to execute their own code on a server. This vulnerability, triggered by an integer overflow, fundamentally undermines the platform's security.
What Administrators Must Do
GitLab has released updates to patch this vulnerability in Community Edition (CE) and Enterprise Edition (EE) versions 19.4.2, 19.3.5, and 19.2.8. The company is urging all organizations hosting their own GitLab instances to update their systems immediately. CISA has added this flaw to its Known Exploited Vulnerabilities (KEV) catalog, underscoring the severity of the threat.
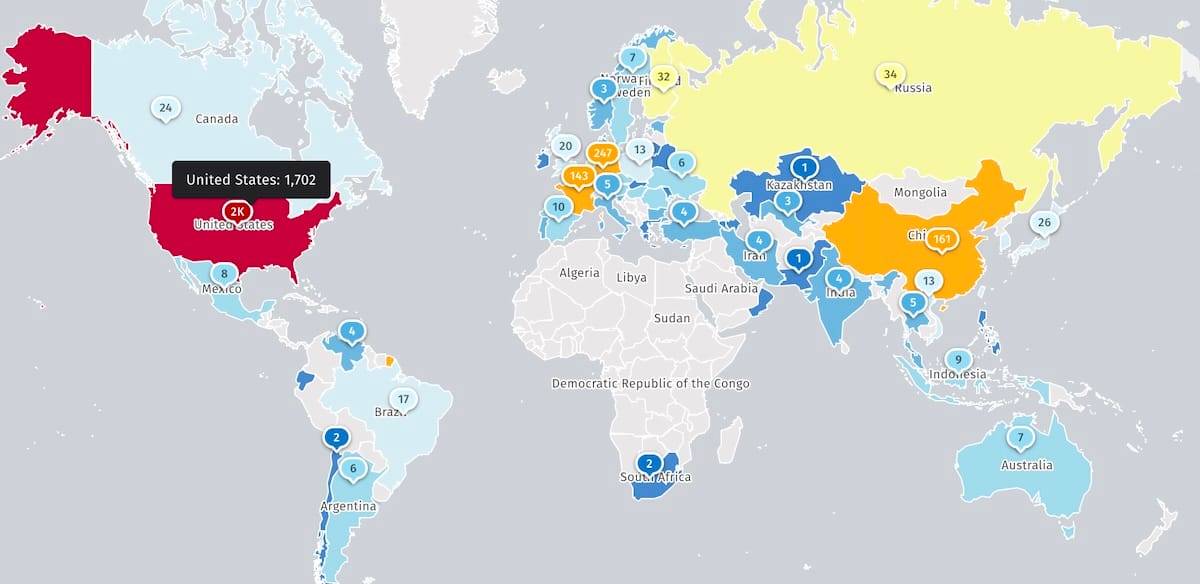
While the official directive currently applies to U.S. federal agencies, cybersecurity experts advise the private sector to prioritize patching this vulnerability. According to data from Shadowserver, there are approximately 2,800 GitLab instances currently exposed to the internet, making them attractive targets for attackers.
Growing Security Challenges
For GitLab, 2026 has been a demanding year regarding security. Several critical flaws have been discovered this year, including vulnerabilities related to authentication bypass and data leakage. The company, which has over 70 million registered users and is used by more than half of the Fortune 100, continues to work to address these challenges.
For users and companies in Georgia utilizing GitLab, this news serves as a reminder that timely software updates are critical. If you are hosting GitLab on your own servers, check your version number and follow the manufacturer's recommendations immediately to prevent potential attacks and data loss.